Large Language Models (LLM)
LLM post-training (SFT & RL). Advancing and benchmarking frontier models in cryptography and cybersecurity.
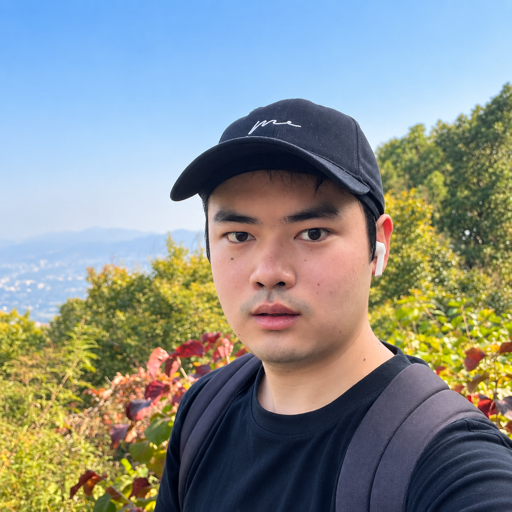
I am a Ph.D. student in cybersecurity at the University of Chinese Academy of Sciences (UCAS), advised by Prof. Xiaorui Gong. I received my B.E. degree in information security from the University of Science and Technology of China (USTC) in 2022. Prior to 2026, I was actively involved in CTF competitions with the NeSE team, focusing on cryptography and blockchain.
My doctoral research focuses on applied cryptography, particularly the Generalized Birthday Problem and its cryptanalytic applications. Now I am focusing on LLM post-training and exploring the intersection of AI and cryptography. I will graduate in June 2027 and am open to opportunities.
LLM post-training (SFT & RL). Advancing and benchmarking frontier models in cryptography and cybersecurity.
Automated cryptanalysis and vulnerability discovery using LLM agents. Currently learning Lean 4 and formal verification for cryptography.
Updates
I expect to complete my Ph.D. in June 2027. I’m looking for postdoctoral or other research positions in LLM post-training, cryptography and AI, or cybersecurity. If you find my research areas matching any opportunity, please feel free to contact me via email.
We released our automated cryptanalysis results found by a MiniMax internal model. See our technical reports in MiniMax Research.
Our joint work on using LLM agents to discover vulnerabilities in cryptographic libraries will be presented at the Black Hat USA 2026 Briefings. See the talk page for details.
Background
University of Chinese Academy of Sciences
Straight-to-PhD. Major in Cybersecurity.
University of Science and Technology of China
MiniMax
Post-training of MiniMax cyber models. Automated Cryptanalysis & AI for Security.
Ant Group
Conducted security analysis of ML-DSA (Dilithium) and its implementation bugs.
Tencent Technology
Automated discovery of cryptography vulnerabilities using LLM agents.
Selected Work
TL;DR: We study structural regularity in the Generalized Birthday Problem and its impact on practical schemes including incremental hashing and Equihash. The main contribution of this work is the complexity analysis of regular and non-regular GBP, with important implications for the $k$-$\textsf{XOR}$ and $k$-$\textsf{SUM}$ problems.
TL;DR: We propose a new list-item-reduction framework that reduces the memory complexity of Wagner’s algorithm from $2nN$ to $nN$ bits, thereby weakening the ASIC resistance of Equihash. This optimization has important implications for the efficient implementation of Wagner-style algorithms.
TL;DR: We extend post-retrieval to Wagner’s $k$-tree algorithm, reducing peak memory from exponential in $k$ to $O(k^2\ell N)$ with only linear time overhead. Applied to preimage attacks on incremental hashes, this trade-off can substantially reduce their memory–time cost.
TL;DR: We disprove Tokareva’s conjecture that every Boolean function on $\mathbb{F}_2^n$ of algebraic degree at most $n/2$ can be written as a sum of two bent functions, constructing explicit counterexamples for all even $n \ge 8$ via large-scale automated reasoning with LLM agents.
TL;DR: We introduce two-bit lifting for ternary SIS, reducing the query complexity of polynomial-time LtHash collision attacks while preserving ternary coefficients. For LtHash16, the attack uses about $2^{81}$ hash queries.
Guannan Wang, Lili Tang, and Guancheng Li Speakers
Institute of Information Engineering, UCAS
Crypto & Blockchain.
USTC
Crypto & Reverse Engineering.
NeSE’s crypto team: tl2cents (me), deebato, and Threonine.
Team: Lili Tang, Chenyu Li, and Hao Jiang
First independent team from mainland China to qualify for DEFCON Finals.